Compliance
Compliance scores tagging, lifecycle, backup-related and configuration checks that FinomateAI evaluates from billing and inventory signals. It is not a replacement for your security auditor.
CloudHealth policies can both evaluate and act (notify, stop, delete) inside a Perspective. FinomateAI compliance evaluates. Remediation happens in AWS, Azure or Google Cloud, not in FinomateAI.
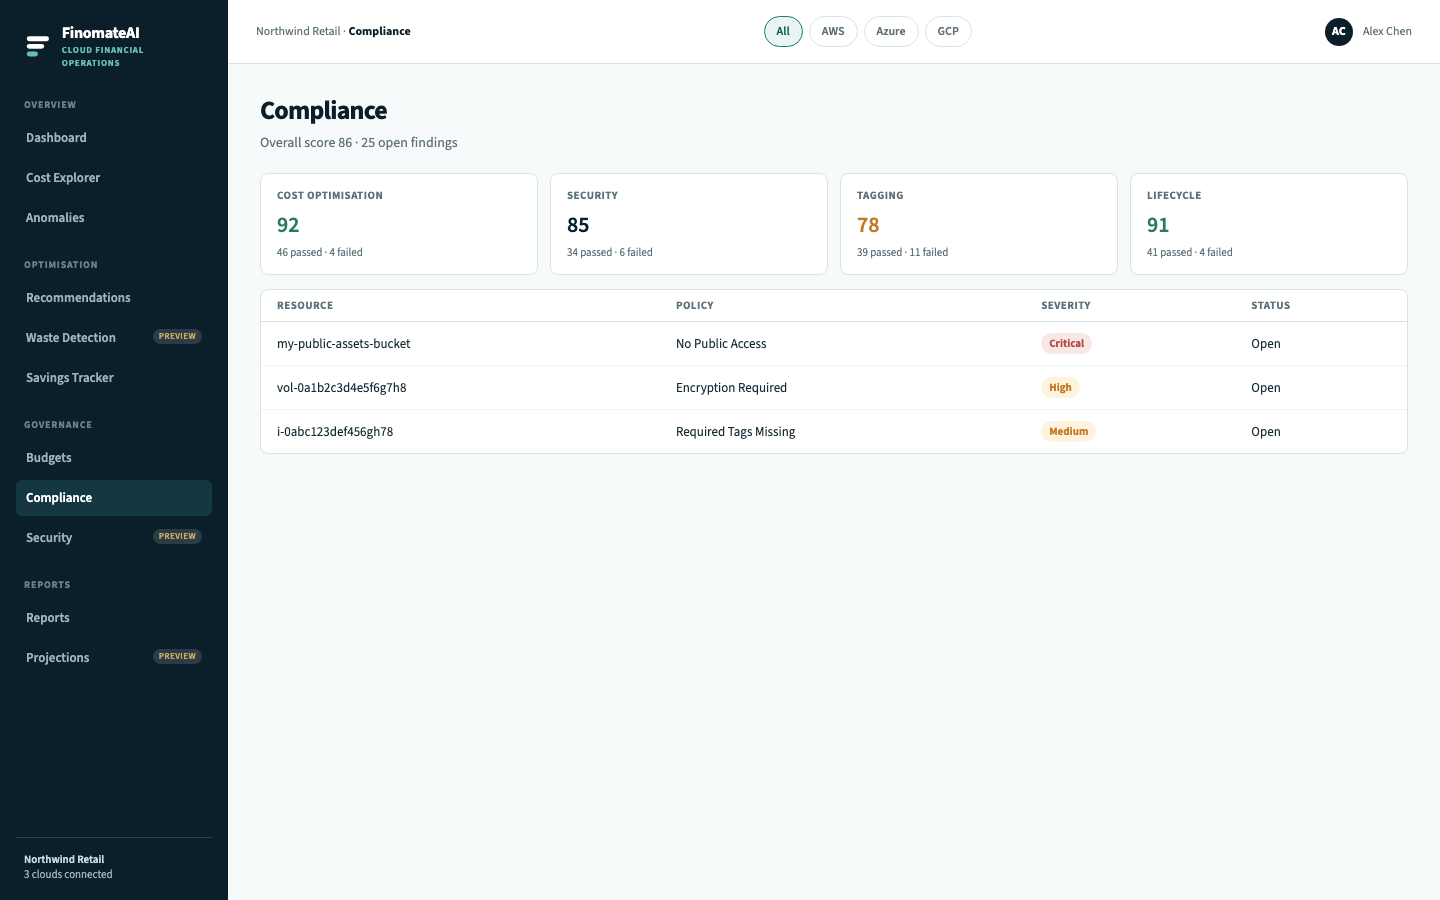
Read the scores
- Open Compliance.
- Note category scores (cost optimisation, security, tagging, lifecycle).
- Open non-compliant resources.
- Assign an owner from the resource tags or account default.
Act
- Tagging failures — fix tags so allocation can work.
- Encryption / public access — treat as security work; see Security findings.
- Idle resources — send the owner to Recommendations.
Expected result
Every open critical finding has an owner and a next review date.